NERC's attempted-compromise definitions fall short

PRC-029 enforcement discretion by RE and CIRCIA's final rule reaches OMB
Welcome to another week of industry insights and resources!
NERC's proposal to make attempted compromises reportable at Low Impact drew between 19% and 37% weighted approval at initial ballot, short of the two-thirds it needs. CISA's final CIRCIA rule is now under review at OMB.
Four Regional Entities have posted how to request PRC-029 enforcement discretion, ahead of the January 1, 2027 design date for non-BES IBRs. Plus a report on internet-exposed solar and wind systems at European renewable sites, two new entries in CISA's Known Exploited Vulnerabilities catalog, and an advisory on end-of-life Hitachi Energy RTU500 firmware.
Also, we look forward to seeing many of you at GridSecCon!
See You at GridSecCon?
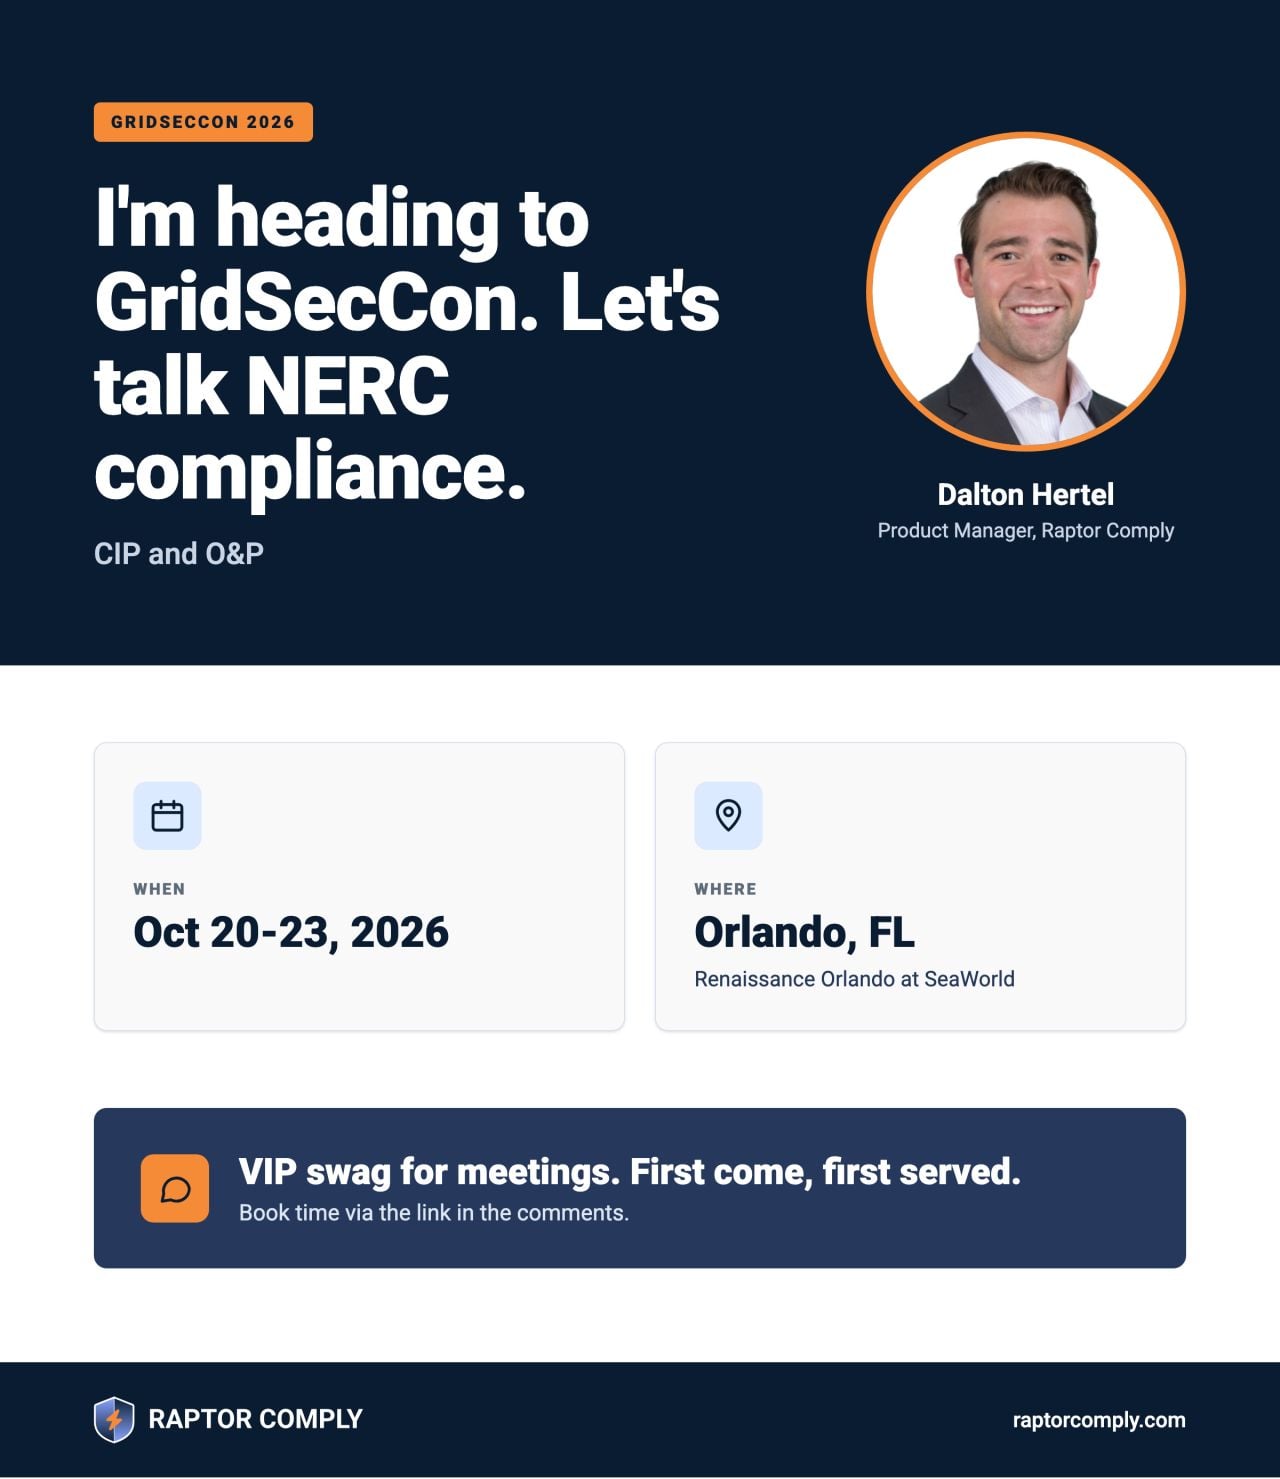
We'll be at GridSecCon in Orlando, October 20-23 and would love to meet you. Dalton will be handing out VIP swag to those who book time:
Industry Update
Attempted-Compromise Definitions Fall Short at Initial Ballot
The initial ballots on Project 2022-05 closed September 23. Every item reached quorum, at 91% or more, and none came near the two-thirds weighted segment approval NERC's Standard Processes Manual requires:
CIP-003-12: 25.32%
CIP-008-8: 22.15%
Attempt to Compromise (new definition): 19.47%
Reportable Cyber Security Incident (revised definition): 22.65%
Implementation plan: 36.60%
These are the changes our September 11 issue covered: a reporting trigger that would reach attempts as well as compromises, extended to Low Impact through CIP-003. NERC says the drafting team will "review all responses received during the comment period and determine the next steps of the project." Under the manual, significant changes mean another formal comment period and an additional ballot, and there are "no limits to the number of public comment periods and ballots."
CISA's Final CIRCIA Rule Is Under Review at OMB
CISA sent its final rule for the Cyber Incident Reporting for Critical Infrastructure Act (CIRCIA) to the White House Office of Management and Budget, which received it on October 1. The text stays private until that review ends.
Once the rule takes effect, covered entities must report a covered cyber incident to CISA within 72 hours and a ransom payment within 24 hours. Who counts as covered is the open question. CISA's 2024 proposal included any entity that already reports cyber incidents under the NERC CIP standards (CIP-003 and CIP-008), plus any entity that files DOE's OE-417 form. The final rule may change that. Until it takes effect, CISA says CIRCIA reporting is not required.
8,547 Exposed Solar and Wind Systems in Europe
Researchers at Modat identified 8,547 internet-exposed systems belonging to solar parks and wind farms across 35 countries in the EU, EFTA and EU candidate states, presented October 6 at the Dutch National Cyber Security Centre's ONE Conference. Some are the management interface of a single turbine; others "control several turbines, or a whole farm, from one screen." Modat published country totals only and notified affected parties through national CERTs. pv magazine reports 7,942 of the systems at solar parks, 2,766 of them in Spain.
End-of-Life Hitachi Energy RTU500 Firmware
CISA published a Hitachi Energy advisory on October 6 covering five vulnerabilities in RTU500 series CMU firmware (CVSS v3 9.8), including unauthenticated firmware upload through the update endpoint. Hitachi Energy says currently supported firmware is not affected, but "there is a likelihood that the end-of-life versions 11.x and prior are affected." End-of-life versions get no security updates; the fix is an upgrade to 12.7.8, 13.9.1 or later.
Compliance Resources
PRC-029 Enforcement Discretion: How Each Region Takes Notice
NERC's practice guide says the ERO Enterprise will "not process potential noncompliance" with the design requirements in R1, R2 and R3 for GOs that seek, but cannot secure, the resources to meet the design compliance date. That notice must reach the Regional Entity prior to their compliance date. Four Regional Entities have posted their intake: WECC, MRO, SERC, and Texas RE. GOs in NPCC and ReliabilityFirst should ask their Regional Entity directly.
Important Dates
Today: Responses due on the DOE's voluntary RFI on Executive Order 14421. Ballot pool also closes for the Standard Processes Manual revisions.
October 13, 2026: NERC Large Loads Working Group meeting, 2:00 to 3:00 p.m. Eastern, to approve the computational load disturbance performance SAR.
October 16-26, 2026: Initial ballot on the Standard Processes Manual revisions.
October 20-23, 2026: GridSecCon 2026, Orlando, hosted by SERC, NERC and the E-ISAC.
October 22, 2026: Comments close on the two Large Loads Working Group SARs.
Join our mailing list.
Weekly industry insights, news, and product updates.
More News
NERC's attempted-compromise definitions fall short
PRC-029 enforcement discretion by RE and CIRCIA's final rule reaches OMB

One-day turnaround on PRC-029-2
Plus CISA and the FBI on third-party ICS integrators
NERC moves on attempted compromises at Low Impact + DOE RFI
Definitions move reportable cyber incidents, DOE wants equipment metadata, Questionnaires in beta

Executive order reaches grid equipment already contracted and installed
FERC tests the paper burden of EOP-004-5, and we launch a SharePoint integration